
Healthcare
Security that keeps care running
Protect patient data and clinical systems from ransomware and breaches, while meeting HIPAA obligations.
Threat landscape
The healthcare threat landscape
Healthcare is a prime target: attackers know a hospital cannot afford downtime, and patient data is valuable.
Ransomware against care
Attacks encrypt clinical systems and force hospitals to divert patients. Inline intrusion prevention stops ransomware before it spreads.
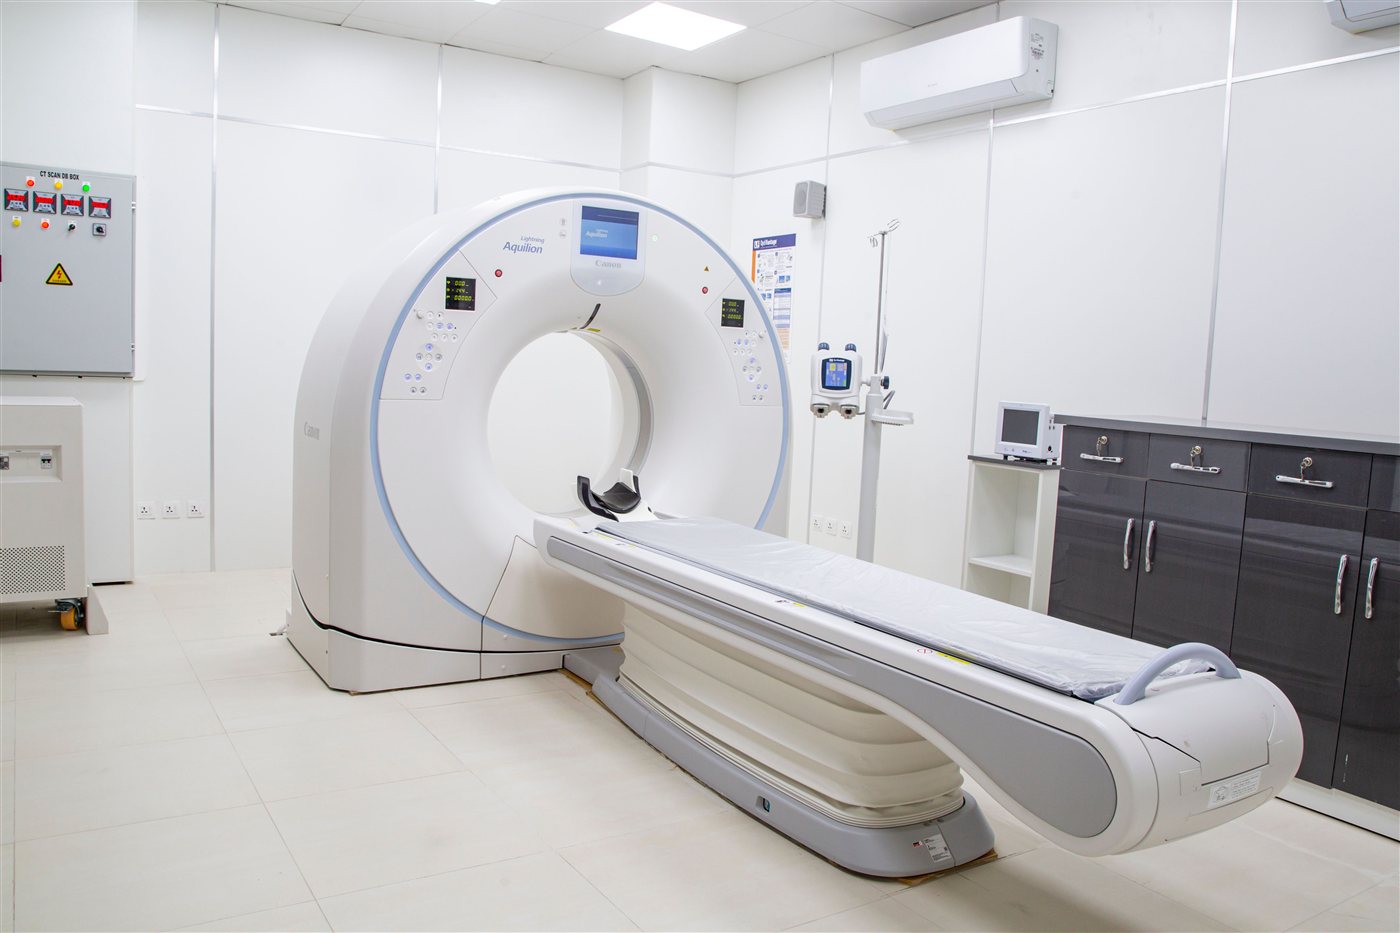
Connected medical devices
Infusion pumps and imaging devices run old, unpatchable software. Network segmentation and firewall controls reduce the risk they carry.
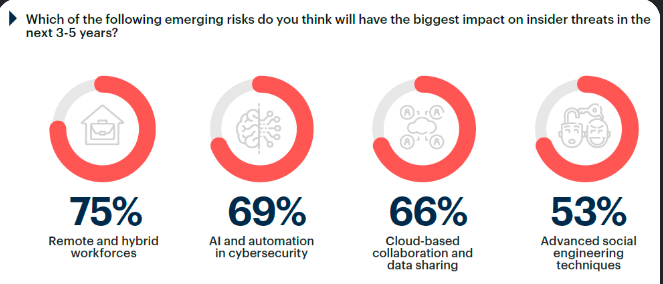
Insider data exposure
More people need access to records than in any other industry, making least-privilege access and audit essential.
Compliance & controls
Meeting HIPAA and beyond
| Requirement | How SecureTrust satisfies it |
|---|---|
| HIPAA Security Rule: Access Control (45 CFR §164.312(a)(1)) | Identity- and context-based least-privilege access restricts who can see patient data. → Universal ZTNA |
| HIPAA: Audit Controls (§164.312(b)) | Centralized log collection and correlation produce a complete audit trail. → SIEM Platform |
| HIPAA: Transmission Security (§164.312(e)(1)) | DLP and TLS inspection protect ePHI in transit across web, SaaS and email. → Data Loss Prevention |
| HIPAA: Risk Analysis (§164.308(a)(1)(ii)(A)) | Continuous vulnerability and configuration visibility supports a defensible risk analysis. → Managed Patch Management |
Outcomes
What you get
Fewer breaches, faster recovery, and audit-ready compliance.
Stop ransomware
Prevent the attacks that force downtime.
Protect ePHI
Keep patient data confidential and intact.
Audit-ready
Prove HIPAA compliance on demand.
Keep systems up
Patch without disrupting clinical workflows.
SecureTrust let us secure our clinical estate without a single minute of unplanned downtime.
Dr. Elena Vasquez · CIO
Trusted across healthcare
FAQ